Checks, ISO 27001, Early access
ISO 27001 readiness, with the statement of applicability built from the check.
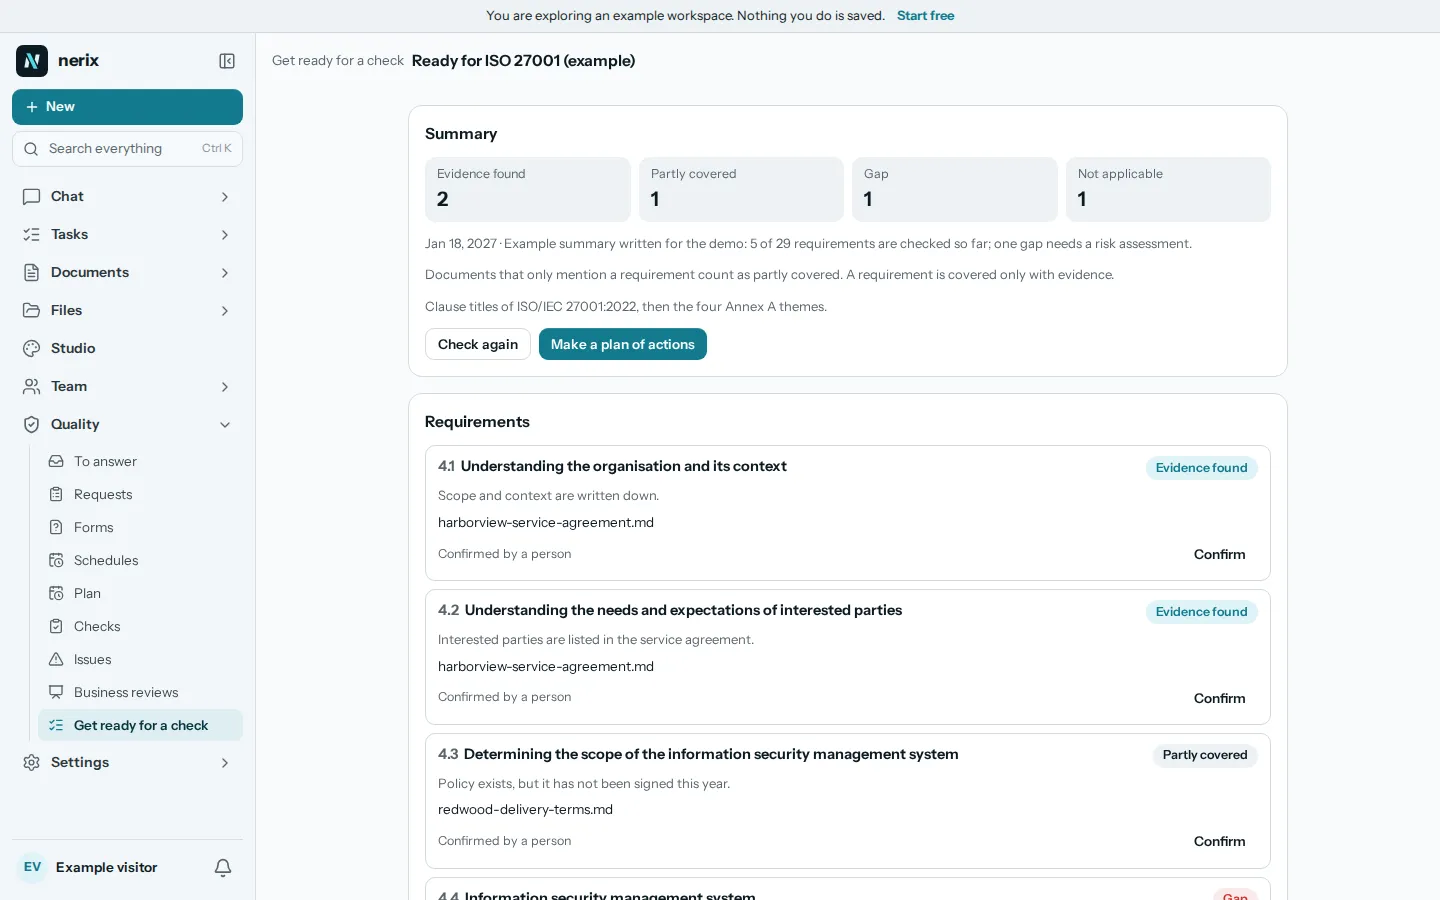
nerix goes through the management system clauses and the Annex A controls of ISO/IEC 27001:2022 and shows, for each one, whether your documents and records show it is in place. The statement of applicability comes from that check, so you never type it twice. Early access.
The free plan is one seat and 3,000 credits a month, never charged.
01What nerix checks
The management system clauses and the 93 controls of Annex A.
The library holds ISO/IEC 27001:2022 with Amendment 1:2024 as the management system clauses (4.1 to 10.x) and the 93 Annex A controls, each with a short label of our own and guidance on what to look for. nerix reads your workspace for each one. A record of work already done counts as evidence, such as an internal check item for that clause recorded as Conforms in the last 12 months, or a held business review for 9.3.
A document that only mentions a control is shown with its passage and counts as Partly found. No evidence at all counts as Not found. A person confirms each result by naming the evidence, and Not applicable needs a reason.
- Management systemContext, scope, leadership, risk assessment and treatment, objectives, competence, documented information, internal audit and management review.
- Organisational controlsPolicies, roles, supplier security, incident management, continuity, legal and contractual requirements.
- People, physical, technologicalScreening, training, remote work, secure areas, access control, backup, logging, secure development.
- Laws that come with itThe standard asks you to know your legal duties. When they apply to you, nerix adds the GDPR, NIS2 and, for high-risk AI, the EU AI Act as locked laws, each saying what requires it.
02Statement of applicability
One row per control, built from the check and never typed twice.
For an ISO 27001 check, owners and admins get the statement of applicability: one row per control with Applies or Does not apply, and a reason when it does not, because an auditor will ask. Then In place, Partly in place, Planned or Not in place, with the number of pieces of evidence and the risks linked to it.
A control is never marked In place without evidence. You can invite an outside auditor by email to see only the checks you choose, with the evidence found, until an end date you set, up to a year ahead. They are free and use no seat, and you can end their access at once.
- Applies or notA reason is required when a control does not apply.
- StatusIn place, Partly in place, Planned or Not in place.
- Evidence and risksThe count of evidence and the risks tied to the control.
- Outside auditorRead only access to the checks you pick, with an end date.
03What nerix sets up
The yearly rhythm of an information security system.
In Settings, Certifications, say you follow ISO 27001 and nerix sets up the information security risk kind, lists for suppliers, scope, legal requirements, changes, communication and drills, and figures such as security incidents, uptime and training done. You see what it would add first, and nothing you have is changed.
It also plans the checks the standard expects, with dates around your audit: an access rights review and a backup restore test twice a year, an incident response tabletop, a vendor security review, a yearly internal audit and a yearly business review.
- ProgrammesInformation security internal audit, access rights review, backup restore test, incident response tabletop, vendor security review, security and privacy review.
- Year planItems tied to clauses such as 6.1.2 risk review, A.5.18 access review, A.8.13 backup test and A.5.30 continuity test.
04Where it stops
It organises the evidence. It does not secure your systems.
nerix reads documents and records. It does not scan your network, test your controls technically or run a penetration test, and it cannot see whether a backup really restores. It can only show that you wrote a procedure, held the test and kept the record. It does not issue a certificate: an accredited certification body does, after its audit. ISO text is paid, so the full clause wording comes from your own copy.
The statement of applicability is built from the check and from your risks. A person still decides which controls apply and why.
Readiness information, not an audit, a certificate or legal advice.
05Questions
Questions
Does nerix make us ISO 27001 certified?
No. A certificate comes from an accredited certification body after its audit. nerix shows where your documents and records already cover the standard, builds the statement of applicability and plans the internal checks.
Can nerix test our security controls?
No. It reads your documents and records. It cannot scan systems or prove a control works, so a control with a policy and a test record is Evidence found only when a person confirms it.
How is the statement of applicability made?
From the ISO 27001 check: one row per control with Applies or Does not apply, a reason for any that do not apply, an implementation status, the evidence count and the linked risks. Owners and admins can change it. A control is never In place without evidence.
Can our auditor see the results?
Yes. Invite an outside auditor by email, choose which checks they may see, set an end date up to a year ahead, and end access at any time. They see only those checks with the evidence found, and they use no seat.
Which version is used?
ISO/IEC 27001:2022 with Amendment 1:2024, with the management clauses and the 93 Annex A controls.
What does a check cost?
The price is shown before you start: credits per requirement checked, plus a one-time charge the first time each document is read. See the pricing page.
Need something this does not do? We build it into your workspace. Built for you
- GDPR data protectionCheck your documents against 38 GDPR duties, from the processing register to breach notification, and find out whether the rules apply to your business.
- NIS2 cyber securityCheck your documents against 35 NIS2 duties, from board oversight to the 24 hour warning and 72 hour report, and see whether NIS2 applies to your business.
- EU AI ActCheck your documents against 45 duties of the EU AI Act, from the register of AI systems to human oversight, and see whether the Act applies to you.
- ISO 9001 quality managementSee which ISO 9001 clauses your documents and records already show, run the internal audits and management review it asks for, and turn gaps into tasks.
- Checks, the whole productThe plan, internal checks, issues and business reviews that every readiness check sits beside.
- TemplatesFree policy, register and checklist templates you can fill in and download.
Keep reading
Quality and audits7 min read
ISO 27001 for small teams, a 90 day plan
ISO 27001 for small teams in plain steps. Who does what, how to scope it, a 90 day plan to audit readiness, what to skip and how certification works.